Full control over your AI workforce
Real-time usage visibility, granular access management, and audit-ready compliance — everything your security team asks for, on one page.
Enterprise-grade controls
Build, test, route, connect and govern — in one place, with your team in control of all of it.
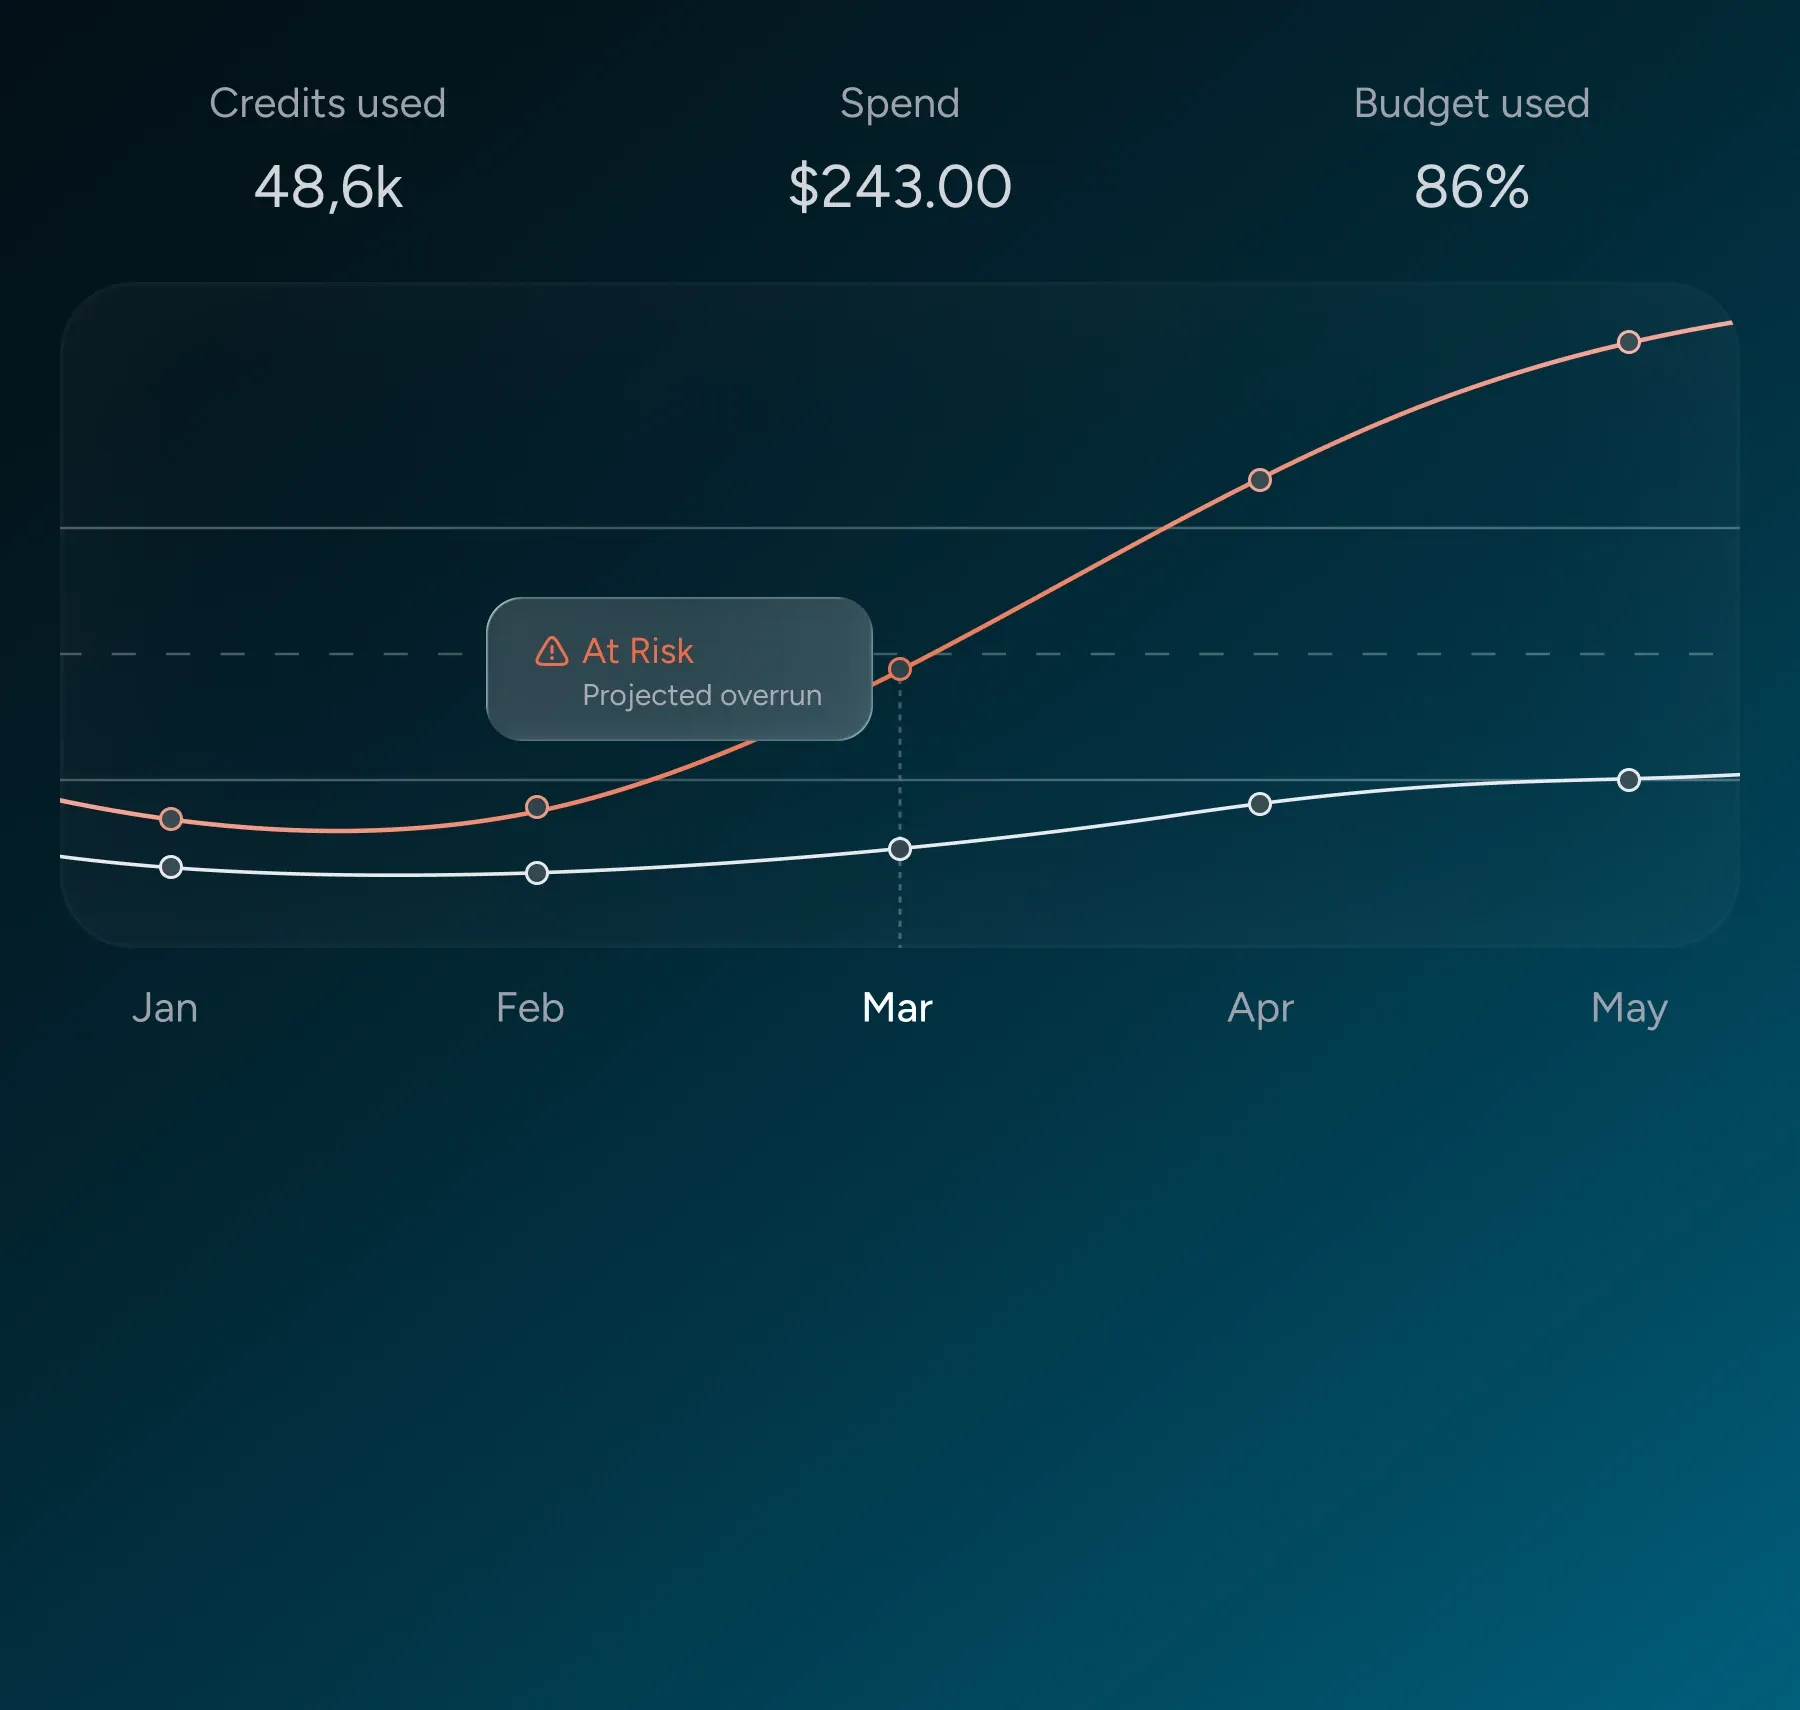
Usage monitoring
Track organization-wide credit usage in real time. Implement budget and quota controls to avoid surprises.
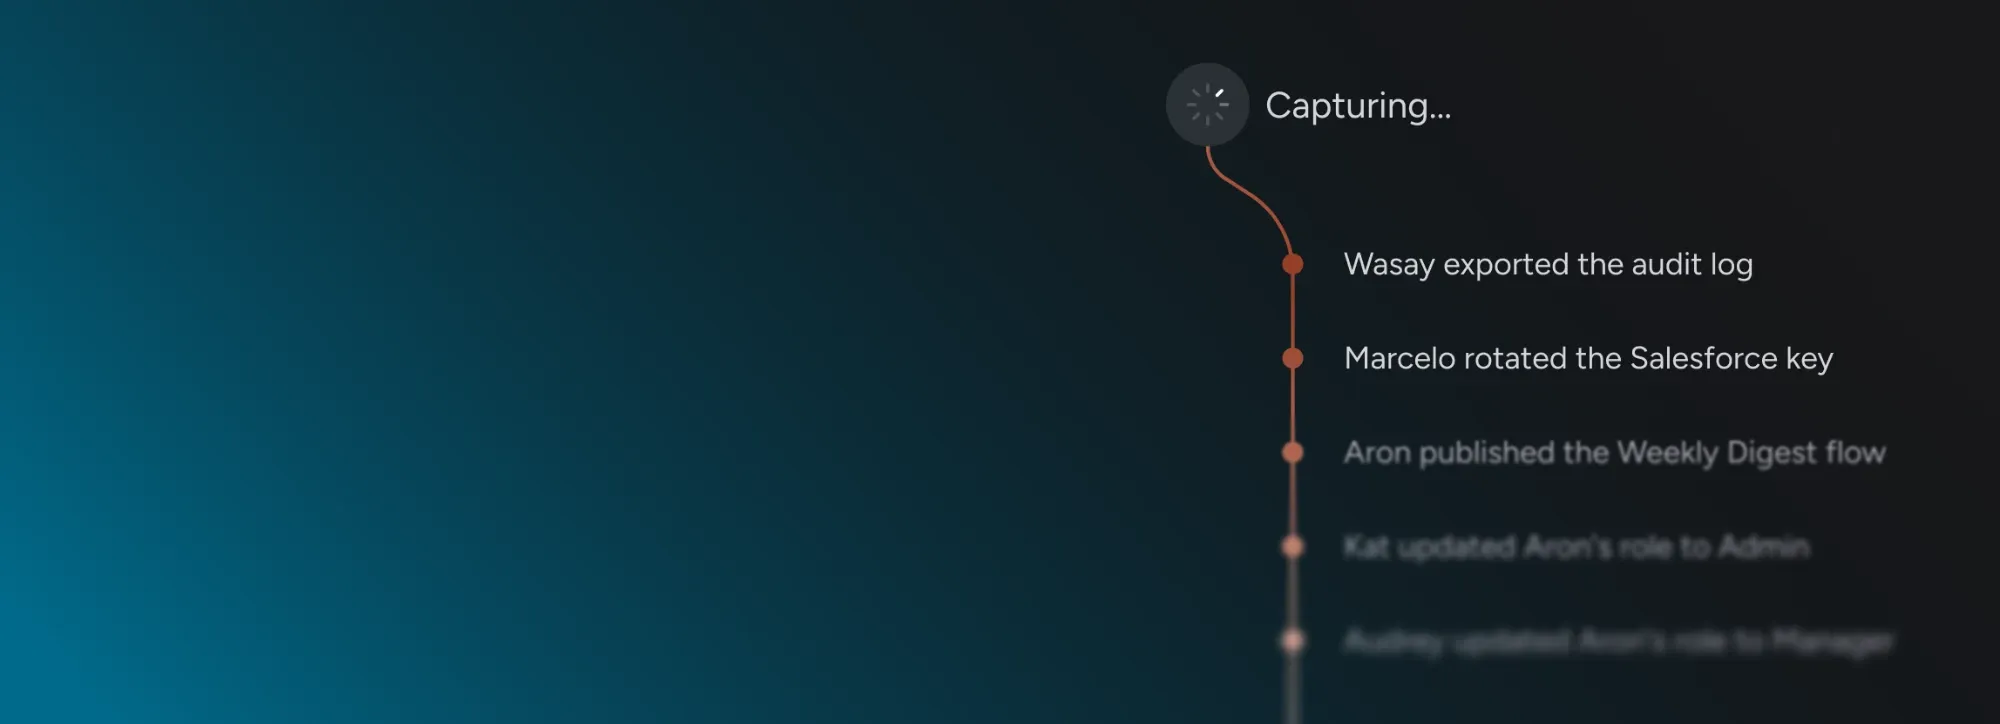
Audit logging
Capture detailed audit trails for actions across the organization to understand where data is flowing.
VPC deployments
Deploy Spaceplace inside your own AWS, Azure, or Google Cloud environment to keep data in your network.
Access management built for compliance
Roles and permissions
Manage reusable roles, credentials, and secrets with scoped access.
SAML SSO and SCIM
Securely streamline identity and access management.
AI model restrictions
Control which AI models teams can use.
SOC 2 Type II
Independently audited and compliant.
GDPR
Zero Data Retention agreements with third-party models.
Common questions, clear answers
Spaceplace applies security, permissions, governance, and guardrails across the platform. Access to enterprise data and actions can be controlled by role, entity, and sensitivity, with audit trails and approval mechanisms supporting traceability and oversight.
Spaceplace uses role-based permissions, entity-level access, action limits, approval flows, and human-in-the-loop controls. The platform determines who can access specific data, which actions they can take, and which actions require approval before execution.
This requires an approved security/legal answer before publication. The current product strategy defines model policies and AI model controls, but it does not specify whether customer data is used for model training or how third-party model providers retain data.
Spaceplace connects with enterprise systems including CRM, ERP, telephony, analytics platforms, documents, email, calendars, communication tools, internal databases, and custom APIs. These integrations give agents governed access to the systems and data they need to operate within enterprise workflows.
Spaceplace is designed around evidence, validation, and evaluation rather than relying on AI responses alone. Critical skills and workflows can be evaluated against defined criteria, while important outputs can include source attribution, confidence, business rules, and human approval for high-risk actions.
Spaceplace supports audit trails, source attribution, approval flows, action limits, execution confirmation, and model policies. This gives enterprise teams visibility into how agents operate and helps keep AI activity governed and traceable across the organization.
Spaceplace supports enterprise access and identity controls including roles and permissions, SAML SSO, and SCIM, alongside enterprise governance capabilities such as audit logging and model restrictions. The Trust page also presents SOC 2 Type II and GDPR as compliance capabilities.
Start with one agent. Expand into a connected team
Typical contract-to-live: 5-10 weeks, depending on integrations and scope.